What are strategies for protecting against two-factor authentication vulnerabilities?
Long time ago, Microsoft admitted that “game is over, if an attacker is landed inside your Active Directory” (“Mitigating Pass-the-Hash and Other Credential Theft”, version 2) by putting the following statement :
“Assuming breach requires a shift in mindset from prevention alone to containment after breach”
Meaning that no security software will help you since that moment. With this statement Microsoft team accepted that 0-Days vulnerabilities and exploits will continue to appear in future. What lessons security architects and experts may learn from Sunburst/Solarwind case? Probably the statement may be expanded to a wider scope:
“Assuming ongoing breach executed in an unidentified past requires a shift in mindset from prevention to continuous containment”.
What if the breach was already happened but we dont know about it now? Cyber-Security vendors now start offering solutions that includes new paradigm :
- Breach Prediction and Threat Intelligence that monitors threat actors in dark net, vulnerabilities and tactics they are going to use. This will allow to identify potential targets and the weaknesses that will be exploited.
- Breach Detection and Response with security controls that will continue to perform even in containment phase (i.e. “game is over”). Make Malware/RAT/APT operators to move in a wrong direction, take “wrong” things, while leaving more Indicator of Compromise and evidences in IT infrastructure.

 We are glad to report that Rohos Logon Key for Mac (v3.7) is compatible with macOS Catalina 10.15.2. We have added dark mode support and ensured authentication functionality for USB drive, YubiKey and Bluetooth devices as a key. Due to a few issues we make this release absolutely free.
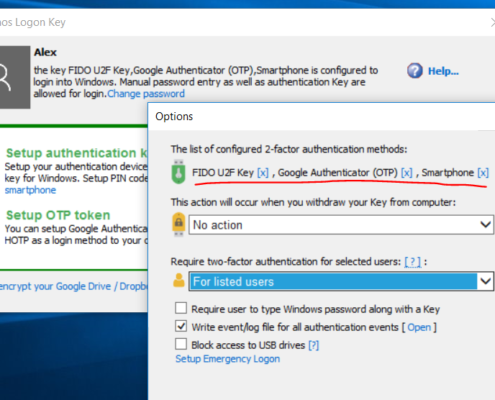
 We have updated Rohos Management Tools v.4.4 adds improvements and bug fixing for Rohos Logon Key v.4.4 in Active Directory network. New Rohos Management Tools allows better MFA management over Active Directory workstations in isolated environments. With Rohos you can use industry accepted RFID cards such as EM, HID Prox, HiTag, Legic, Mifare as a second/single factor logon method for workstation/HMI terminals.
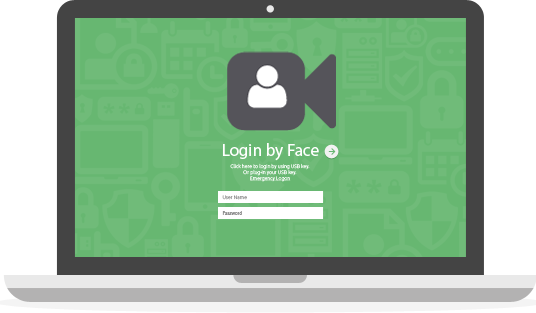 We are glad to announce new update for Rohos Face Logon that allows to set adaptivity level for face recognition. This allows quicker login in any lighting conditions.